Imagine having the power to seamlessly connect your applications, enhance security, and streamline user authentication—all through consuming a Web API hosted in Identity Server. This isn’t just a technical possibility; it’s a strategic move to boost your application’s capabilities and user experience.
You might wonder, how can you effectively tap into this potential? Whether you’re a seasoned developer or just starting, understanding how to integrate and consume these APIs can be a game-changer for your projects. You’ll discover practical steps and insights to confidently navigate and leverage Web APIs hosted in Identity Server.
Get ready to unlock the full potential of your applications and elevate your expertise to a new level. Keep reading to transform your approach and empower your development process.
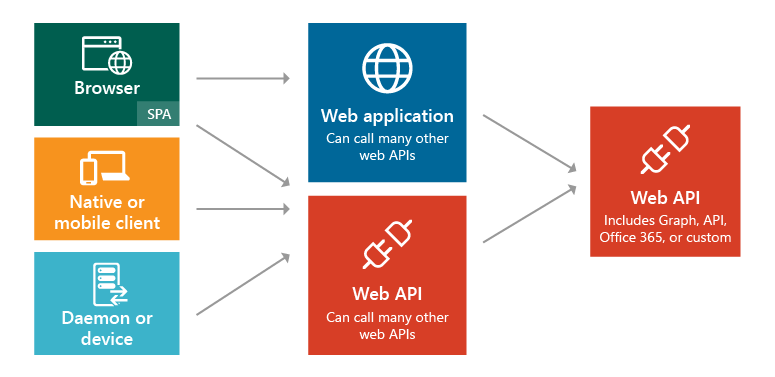
Credit: learn.microsoft.com
Setting Up Identity Server
Accessing a Web API in Identity Server involves secure connections and token-based authentication. Start by obtaining the API’s access token. Use this token in your requests to ensure secure communication with the server.
Installing Identity Server
Start by downloading the Identity Server package. Follow the instructions in the setup guide. It’s important to install all required dependencies. Make sure your system meets all the requirements. You will need a stable internet connection. Once installed, verify the installation. Use the command line to run a simple test. This ensures everything is working well.
Configuring Basic Settings
Open the configuration file. Add your server’s base URL. Set up the security protocols. These keep your data safe. Choose the authentication method. This can be password-based or token-based. Save all the changes. Restart the server to apply them. Check the logs for errors. Fix any issues before proceeding.
Creating Client Applications
Register a new client in the server. This client will access your API. Give it a unique client ID. Set a secret key for authentication. Define the redirect URLs. These are used for successful login. Set the access permissions. Decide what resources the client can use. Save the client details. Test the client by making a request. Ensure it connects to the API successfully.
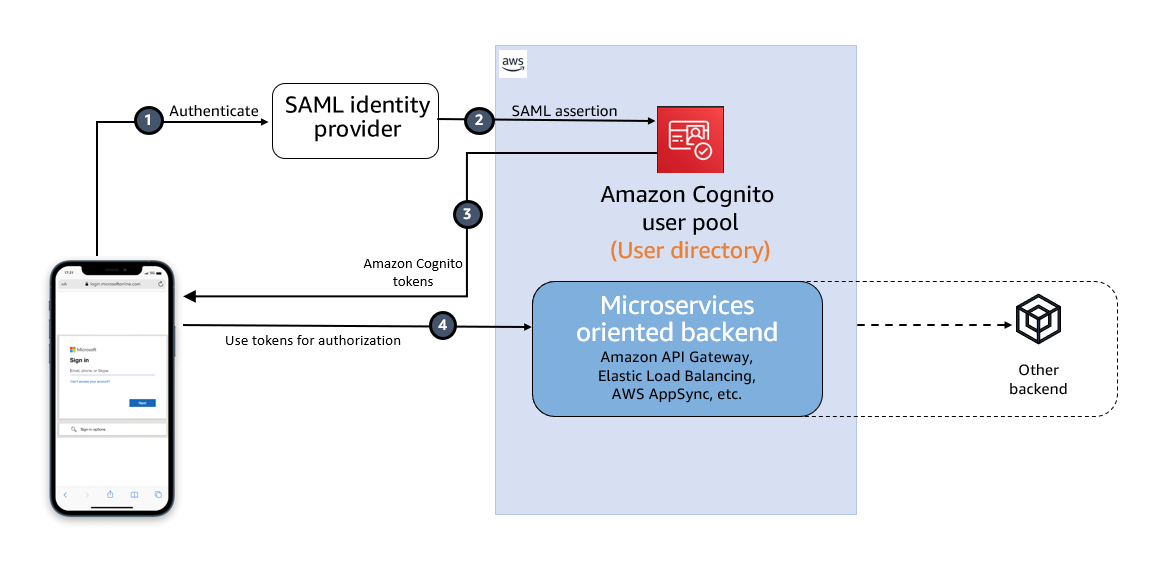
Credit: aws.amazon.com
Understanding Oauth2 And Openid Connect
OAuth2 is a method to give access to users. It makes sure that users get only the right data. Users do not need to share their passwords. This makes it very safe. OAuth2 lets users log in with Google or Facebook. This is easy and fast.
OpenID Connect is built on OAuth2. It adds an identity layer. This helps to know who the user is. It gives more data about the user. Like their name and email. OpenID Connect is simple and flexible. It works with many apps and websites.
OAuth2 is for access control. OpenID Connect is for identity. OAuth2 does not know who the user is. OpenID Connect knows and provides user info. Both help in keeping data safe. But they have different jobs.
Securing Web Apis
Authentication keeps your API safe. It checks who is using your API. Users need to prove who they are. This is done with a username and password. Sometimes, other info is needed too. This keeps bad people out.
A token is like a key. It opens doors but only for a short time. Users get tokens after proving who they are. The token tells the API, “This user is okay.” After some time, the token stops working. Then users need a new one.
Scopes say what users can do. They are like rules. Permissions give users the right to do things. For example, read data or change data. Scopes and permissions keep your API safe. They stop users from doing bad things.
Consuming Web Apis
A HTTP client helps talk to the web server. Choose a good one. Many people like using HttpClient for its ease. It makes sending requests simple. Installing it is easy. Use package managers like NuGet. Configure it well. It should know where to find the API. Point it to the right address. Use the correct port. This is important.
Tokens are like keys. They allow access. Without a key, doors stay closed. Get your token from the Identity Server. It keeps the API safe. Use OAuth or similar methods. Save the token safely. Never share it with others. Send the token with every API request. Place it in the header. The server checks it.
Start with the GET method. It asks the server for data. Use POST to send data to the server. PUT changes existing data. DELETE removes data. Always check the response. It tells if the request worked. Look for status codes. Codes like 200 mean success. Errors show different codes. Fix them when they appear.
Error Handling And Logging
API errors happen often. Network issues are common. Timeouts can occur, too. Sometimes, data is missing. Invalid data can cause errors. Unauthorized access is another problem. Many errors can be fixed. Error codes help understand problems. Error messages can be useful. Handling errors is important.
Retry logic helps when errors happen. It tries again after a failure. Retries can fix temporary issues. Network errors can be solved this way. Retry policies decide how many tries. Some APIs allow limited retries. Exponential backoff is used often. This means waiting longer each time. Retry logic helps keep systems running.
Logging records API activity. It tracks every call made. Logs help find problems. They show what happened. Monitoring watches API performance. It checks speed and errors. Alerts can notify issues quickly. Good monitoring keeps services healthy. Logs and monitoring are key for strong systems.
Testing And Debugging
Unit testing helps ensure that your web API works well. Write tests for each API function. This finds bugs early. Mock objects can be used to test in a controlled way. These are fake parts that stand in for real ones.
Authentication problems can be tricky. Log all requests and responses. This helps find where things go wrong. Check if the tokens are valid. Invalid tokens often cause issues. Review the server logs for error messages. These logs give clues to solve problems.
Postman is a tool for testing APIs. Send requests to your API easily. It shows the response clearly. Check the status code and body. This helps in understanding what went wrong. You can also save requests for later. It’s handy for repeated tests.
Best Practices
Protect your data. Use HTTPS for communication. Check authentication tokens regularly. Keep software updated. Monitor for threats. Limit user access. Use firewalls effectively. Encrypt sensitive information. Always validate input. Ensure strong passwords.
Improve response time. Reduce data size. Use caching wisely. Avoid unnecessary calls. Compress data effectively. Minimize latency. Optimize server settings. Check for bottlenecks. Test regularly. Keep endpoints efficient.
Think big. Plan for growth. Use load balancers. Distribute traffic evenly. Implement horizontal scaling. Monitor server loads. Scale databases as needed. Consider cloud solutions. Ensure seamless integration.

Credit: stackoverflow.com
Frequently Asked Questions
How To Consume Web Api In Web Application?
Use AJAX or Fetch API to send HTTP requests to the Web API. Parse the JSON response. Integrate the data into your web application’s UI. Ensure proper error handling and security measures for seamless functionality.
Can Web Api Be Self Hosted?
Yes, Web API can be self-hosted. Use frameworks like ASP. NET Core to host APIs on local or dedicated servers. This offers more control, customization, and security compared to cloud hosting options. Self-hosting requires server management skills and infrastructure setup for optimal performance.
How To Implement Identity In .net Core Web Api?
Implement identity in. NET Core Web API using ASP. NET Core Identity. Add necessary NuGet packages, configure services, and set up user authentication. Use IdentityDbContext for database operations. Create models for users and roles. Use middleware for authentication and authorization.
Ensure proper configuration in Startup. cs for seamless integration.
How To Consume Web Api Using Httpclient?
Use HttpClient to send HTTP requests to the Web API. Install HttpClient, create an instance, and configure the request. Send the request using GetAsync, PostAsync, or other methods. Handle the response by reading content and checking status codes. Dispose of HttpClient to release resources.
Conclusion
Consuming a Web API hosted in Identity Server is straightforward. Start by understanding the server’s authentication process. Next, ensure your API requests include proper tokens. This guarantees secure access. Explore tools for testing API calls. Postman is a popular choice.
Test thoroughly to avoid errors. Keep documentation handy for reference. Troubleshooting becomes easier. Follow best practices for optimal results. Security is crucial, prioritize it in your setup. Stay updated with Identity Server changes. This helps maintain compatibility. With these steps, interacting with Web APIs becomes efficient and secure.
Your projects will benefit greatly.